 Thailand
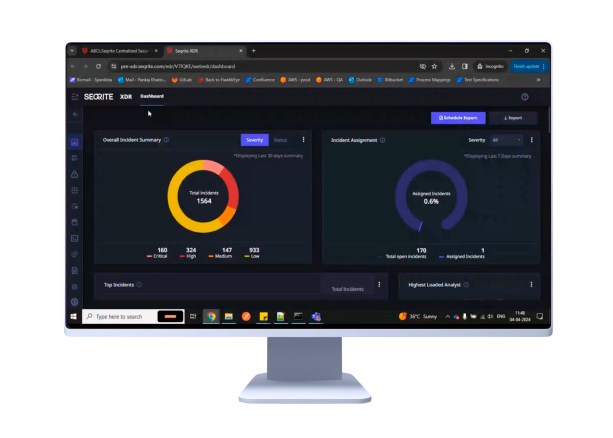
Seqrite XDR overview
Cyber threats keep getting smarter — evasive malware, zero-day, fileless and targeted attacks are hard to catch because detection means correlating data from many sources. Seqrite XDR (Extended Detection and Response) collects data from security products into a centralized security operations platform and uses analytics and automation to centralize, normalize and correlate it, enabling real-time protection across control points, less complexity and a hybrid SOC at a reasonable cost.
Seqrite XDR also detects malicious encryption processes and blocks them before they disrupt the network.
What it connects to
XDR ingests data from Seqrite products — Endpoint Protection, ZTNA, Data Privacy, centralized security management and EMM — as well as third-party sources such as SIEM, firewalls, cloud protection and email gateways, giving one view of an incident along the whole attack path.
Key capabilities of Seqrite XDR
One unified platform
Brings advanced threat detection and response into one platform instead of juggling tools.
Accurate, with fewer false positives
Focused data sources and detection logic reduce false alerts.
SOAR automation and playbooks
Automates triage and response through playbooks to use resources efficiently.
Multi-layer ML/AI protection
24×7 monitoring, behavior anomaly detection, automatic incident correlation and severity optimization.
Response and SLA management
Manage incidents, track SLAs and use detailed SOC dashboards.
Shared threat intelligence
Combines global threat intelligence with Seqrite’s in-house research to address zero-day and APT threats.
Historical search
Search historical data for IOCs to find incidents you may have missed; Seqrite states events and alerts can be retained for up to about 180 days.
MDR team support
Seqrite’s MDR team helps with response and extends your SOC.
User behavior analytics (UBA)
Real-time behavior monitoring
Watches sign-in activity for signs such as impossible travel or unexpected locations.
AI-driven anomaly detection
Uses machine learning to flag activity such as sign-ins from non-compliant devices or single-factor authentication.
Insider-threat alerts
Alerts on possible account compromise from risky user behavior.
Integrated insights and less alert fatigue
Correlates user anomalies with endpoint and network data and focuses on high-risk activity to cut false positives.
Why choose Seqrite XDR
Strengths as stated by Seqrite include more than 20 years of endpoint protection experience, an in-house research lab that produces up-to-date IOCs and rules for local and regional threat actors, cost-optimized data storage, a design aligned with SOC processes, and automation that reduces triage workload. Seqrite reports at least 30% less triage effort and over 50% fewer alerts; actual results depend on each environment.
Seqrite XDR holds the AV-TEST Approved Advanced Endpoint Detection & Response mark for Windows (07/2024 test), and helps MSSPs run managed detection and response with fewer resources.
Use cases and FAQ
Who is XDR for?
Organizations replacing separate EDR and SIEM, finance and healthcare firms detecting multi-stage attacks, MSSPs, and small security teams that want less alert triage.
What is the difference between XDR and EDR?
EDR covers endpoints, while XDR extends to network, cloud, email and user identity.
Do we need our own SOC?
No. You can add Seqrite MDR services to extend your team.
How long does deployment take?
It depends on device count and the data sources to connect; we provide a plan after assessing your requirements.
Specifications on this page are based on Seqrite’s published product datasheet (2024). Editions, versions and features may change — please confirm with our sales team before ordering.
Why buy and deploy through our team
We are a Thailand-based team providing consulting, supply, installation and after-sales support for Seqrite. We work in Thai and English from requirements assessment, quotation and proof of concept (POC) to administrator training.
Request a quote and demo
Contact our sales team for a free quote and demo. We reply within one business day through the “Get a Quote” page or by phone.