 Thailand
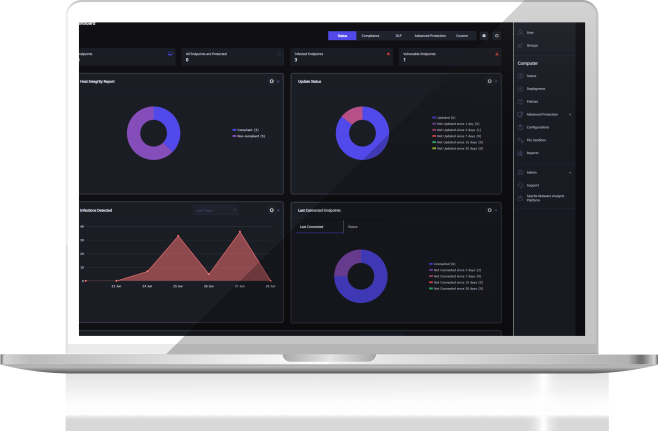
Seqrite EDR overview
As organizations in both public and private sectors become targets of advanced threats, traditional endpoint protection often lacks the visibility to detect and respond in time. Seqrite EDR (Endpoint Detection and Response) addresses this by continuously collecting data from hardware, operating systems and applications, so security teams can review alerts and past events, query endpoints for fresh data, and respond automatically or manually.
Core capabilities of Seqrite EDR
Multi-stage inspection
Analyzes system events through layered behavior analysis, signature matching and ML-based detection.
Online and offline network support
Supports air-gapped and highly restricted networks; rules, behaviors and IOCs can be updated, and automated policy-based response also works offline.
Automated and manual IOC hunting
Search historical data for IOCs using the latest threat intelligence from Seqrite’s team and government bodies such as CERT-IN.
Rule builder
Create organization-specific rules to catch MITRE-aligned or unusual activity in your environment.
Risk-based response policy orchestration
Define real-time and offline response actions with scoped automated response based on risk, using standard or custom policies.
Investigation desk
Drill into incident details and context, query live system data, and follow alert lists and alert maps from one place.
Incident management
Manage incidents through incident lists and endpoint and user data, and define remediation actions.
Advanced alerting, dashboards and reports
Integrates with SIEM and sends SMS/email alerts, with dashboards for system health, critical incidents, impacted events and false-positive rate, plus reports aligned to MITRE TTPs.
Benefits of Seqrite EDR
Stop advanced attacks
Telemetry from sensors goes through multi-stage analysis, and suspicious activity can be blocked immediately.
Stop malware before it spreads
Real-time automated actions such as isolating a device or stopping a process greatly reduce the chance an attack succeeds.
Deeper investigations
Captures script executions, commands and sequences so analysts triage faster and compliance needs are supported.
Less reliance on outside forensics
Security and IT teams can investigate attacks in detail on their own.
Hunt hidden threats in historical data
Advanced attackers can hide for months; event storage combined with threat hunting and threat intelligence helps find and respond to them.
System requirements (on-premises version)
| Component | Requirement |
|---|---|
| Windows (64-bit) | Windows 8.1, 10, 11, Server 2012, 2016, 2019, 2022 |
| macOS | Intel Core or Apple M1/M2/M3 — macOS 10.14, 10.15, 12 and 14 |
| Linux (64-bit) | Fedora 32, Linux Mint 20, Ubuntu 17.04/20.04/22.10, CentOS 8/8.2, RHEL 8.1/8.2/9.1, openSUSE 15.1, Rocky Linux, Boss 8 |
| Server (up to 1,000 endpoints) | 3 servers: Worker 40 cores / 96 GB RAM / 3.7 TB disk, Master 4 cores / 8 GB / 500 GB, Update Manager 2 cores / 4 GB / 50 GB — all on Ubuntu 22.04 LTS |
Specifications on this page are based on Seqrite’s published product datasheet (2024). Editions, versions and features may change — please confirm with our sales team before ordering.
Certification and use cases
Seqrite holds the AV-TEST Approved Advanced Endpoint Detection & Response mark for Windows (07/2024 test). Typical use cases: organizations hit by ransomware that need faster detection, IT teams starting a security function, and agencies needing EDR for isolated or offline networks.
Frequently asked questions
How is EDR different from antivirus and Endpoint Protection?
Antivirus focuses on blocking known threats, while EDR focuses on visibility, investigation and response. EDR capabilities are also available in the EDR edition of Seqrite Endpoint Protection.
Can it run on networks without internet access?
Yes. Seqrite EDR supports offline networks, including updates to rules, behaviors and IOCs and automated response.
What server sizing is required?
The on-premises version supports up to 1,000 endpoints per deployment using three servers as listed above; we help size it for your environment.
Do we need a SOC first?
No. If you lack a monitoring team, consider Seqrite MDR alongside EDR.
Why buy and deploy through our team
We are a Thailand-based team providing consulting, supply, installation and after-sales support for Seqrite. We work in Thai and English from requirements assessment, quotation and proof of concept (POC) to administrator training.
Request a quote and demo
Contact our sales team for a free quote and demo. We reply within one business day through the “Get a Quote” page or by phone.