 Thailand
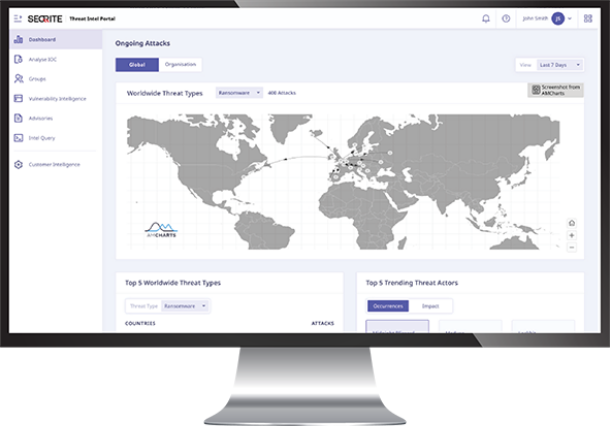
Seqrite Threat Intelligence overview
Seqrite Threat Intelligence delivers threat information and indicators of compromise (IOC) that help security teams stay ahead of trends and defend proactively. The data can enrich detection in your EDR, XDR, SIEM or firewalls.
Key features and benefits
IOC feeds
Indicators such as IPs, domains and hashes to block or hunt across your systems.
Detection enrichment
Adds context to alerts so you can prioritize better.
Awareness of threat trends
Track techniques and threat groups relevant to the region.
Continuous updates
Data is refreshed regularly so it stays actionable.
Use cases for Thai organizations
SOC teams improving detection quality.
Organizations hunting retroactively for IOCs after new threat reports.
Security service providers needing extra data for customers.
Frequently asked questions
How is threat intelligence different from EDR?
Threat intelligence is data about threats, while EDR is an endpoint detection tool; together they give better results.
Can it integrate with existing tools?
We assess integration with your SIEM or firewalls before proposing a plan.
How do I request a quote?
Contact our sales team through the form or by phone.
Why buy and deploy through our team
We are a Thailand-based team providing consulting, supply, installation and after-sales support for Seqrite solutions. You can work with us in Thai or English throughout — from requirements assessment, quotation and proof of concept (POC) to administrator training and on-site troubleshooting.
How deployment works
We start by surveying device counts, operating systems and your most important risks. We then pilot with a small group, tune policies, and roll out across the organization in phases to limit user impact, finishing with documentation handover and administrator training.
Request a quote and demo
Interested in this solution for your organization? Contact our sales team for a free quotation and demo. We reply within one business day through the “Get a Quote” page or by phone.